Every certificate, tracked and renewed.
ArkionID keeps track of every security certificate your company uses. It shows you which ones are about to cause trouble, issues new ones from the provider you choose, and lets you cancel any of them.
A certificate is a digital ID card for a website, server or app. It proves the thing you are connecting to is genuine. A large company runs thousands of them, and every one has an expiry date. When one expires and nobody notices, a website or service stops working.
See every certificate in one place
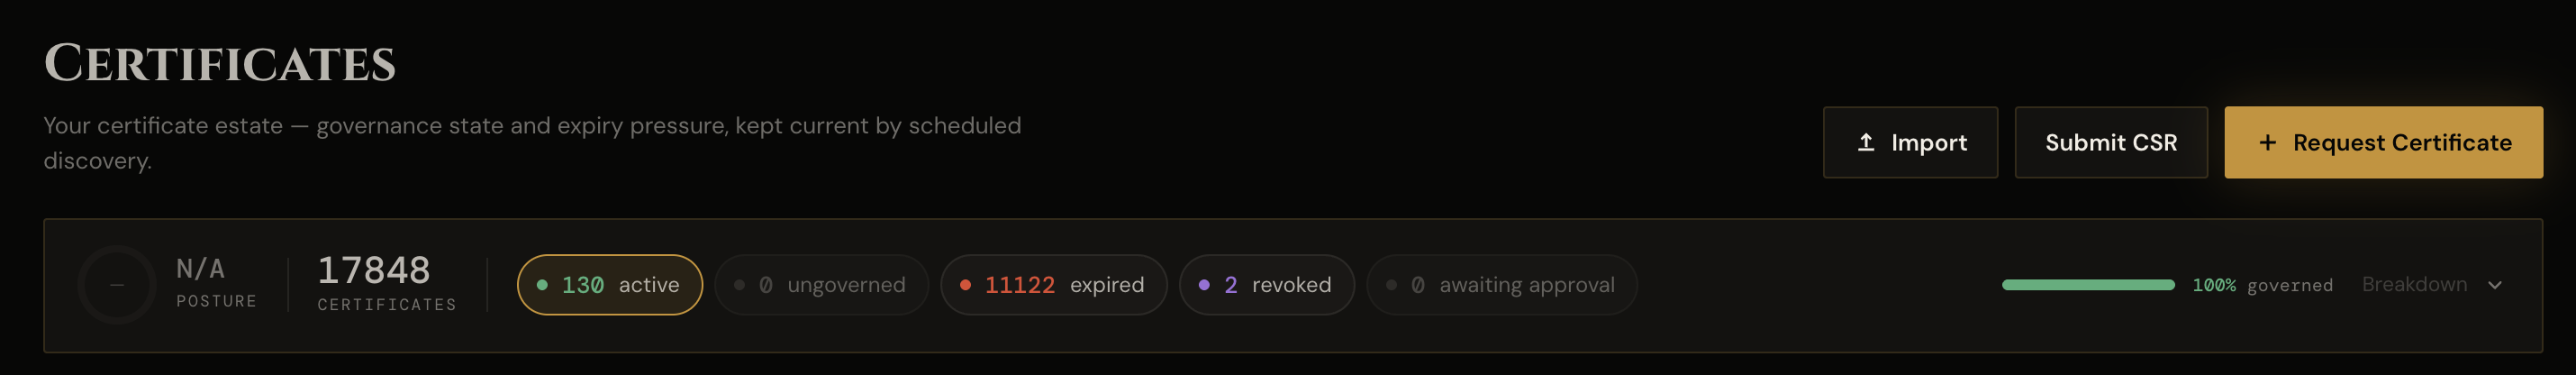
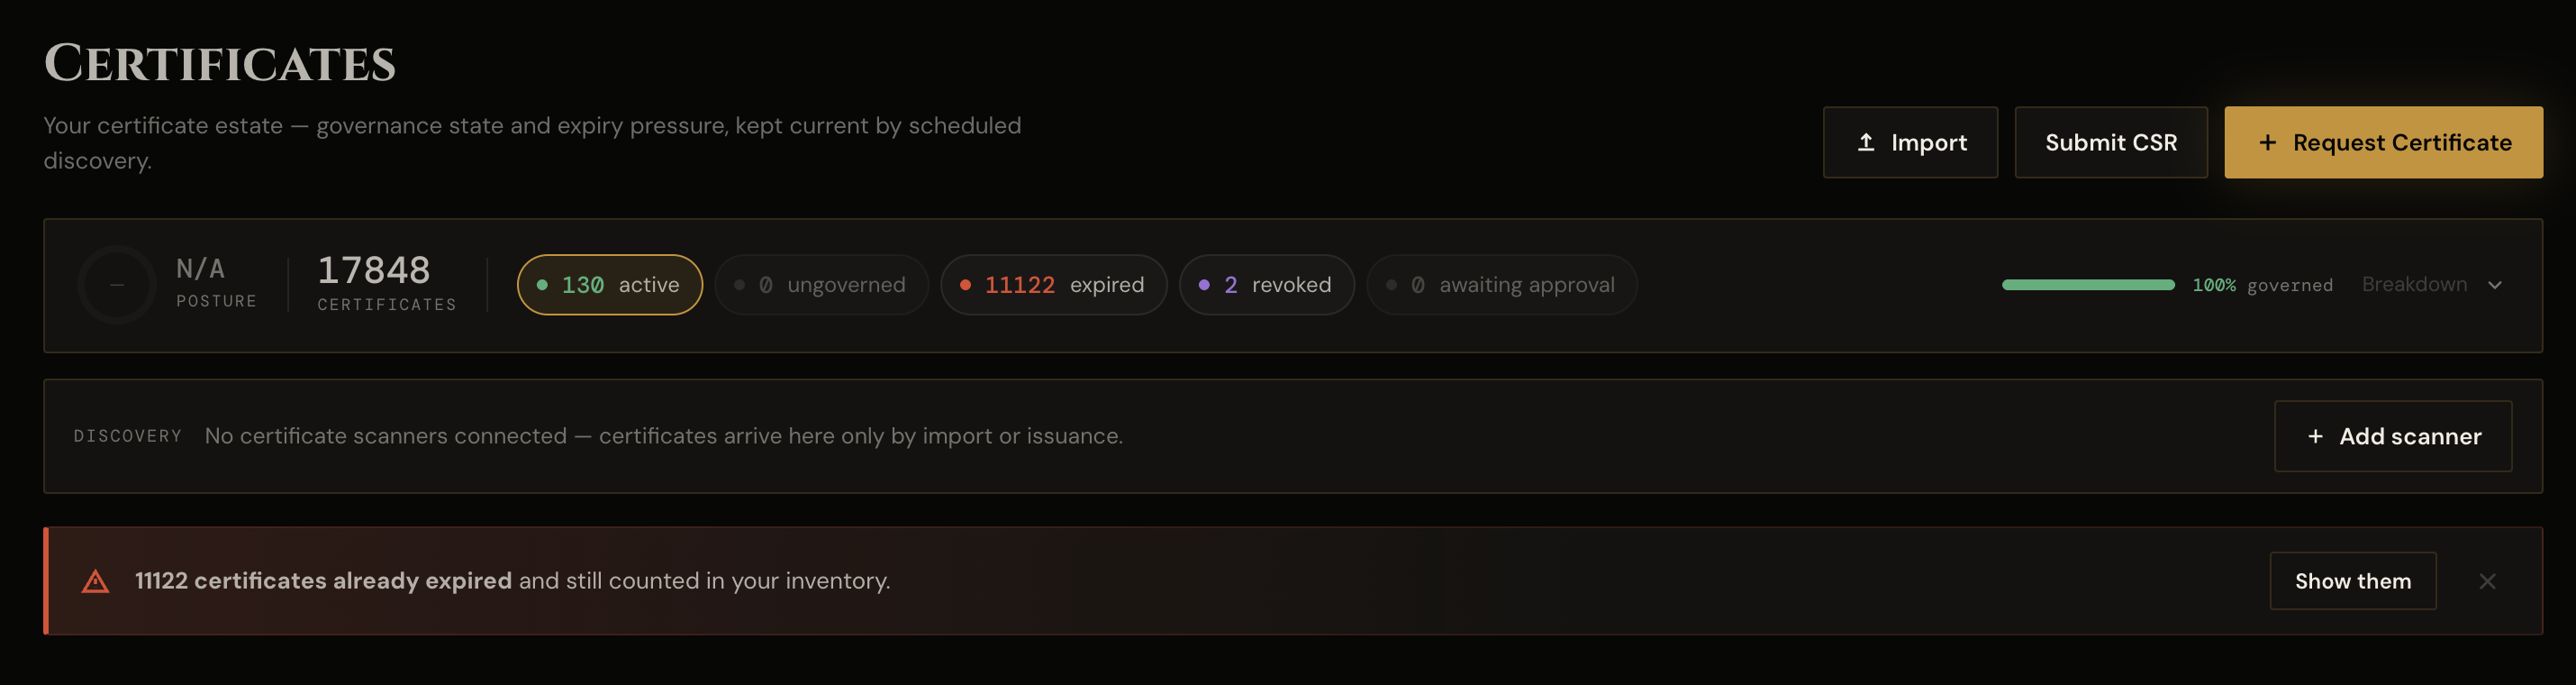
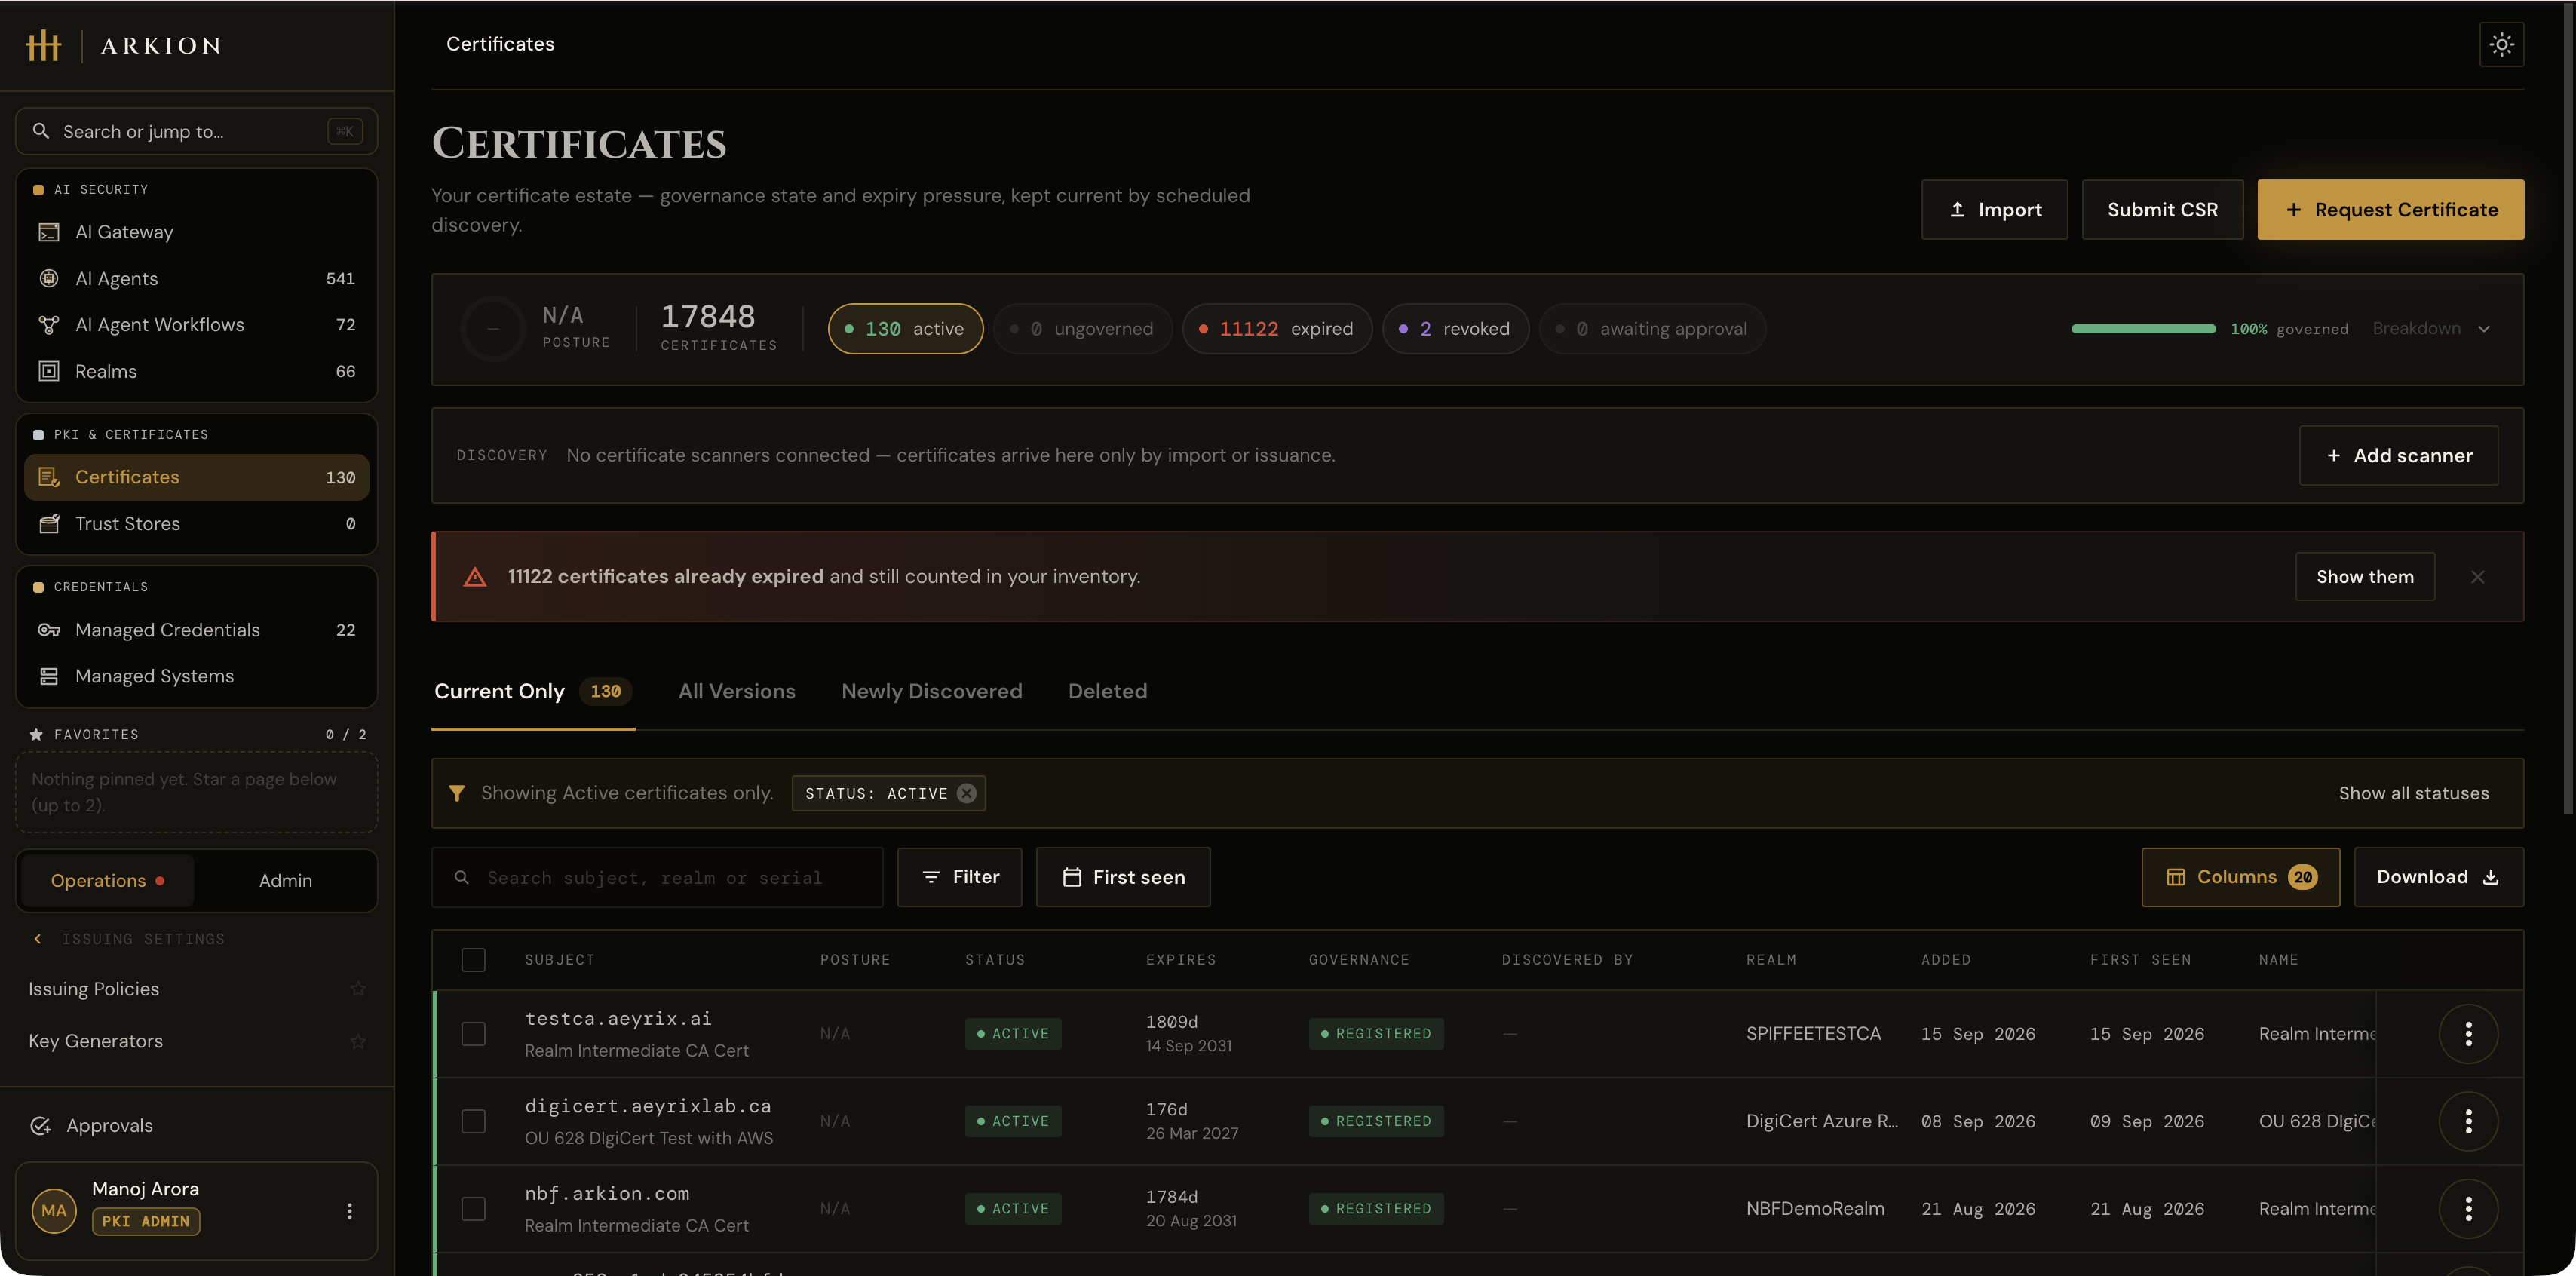
Bring in the certificates you already have, or request new ones, and ArkionID shows them all on one screen: how many are working, how many have expired, and how many were cancelled.
Spot expired certificates before they cause an outage
An expired certificate is one of the most common reasons a website or service suddenly stops working. ArkionID flags every expired certificate, so nothing runs out without someone knowing.
Use the certificate provider you already trust
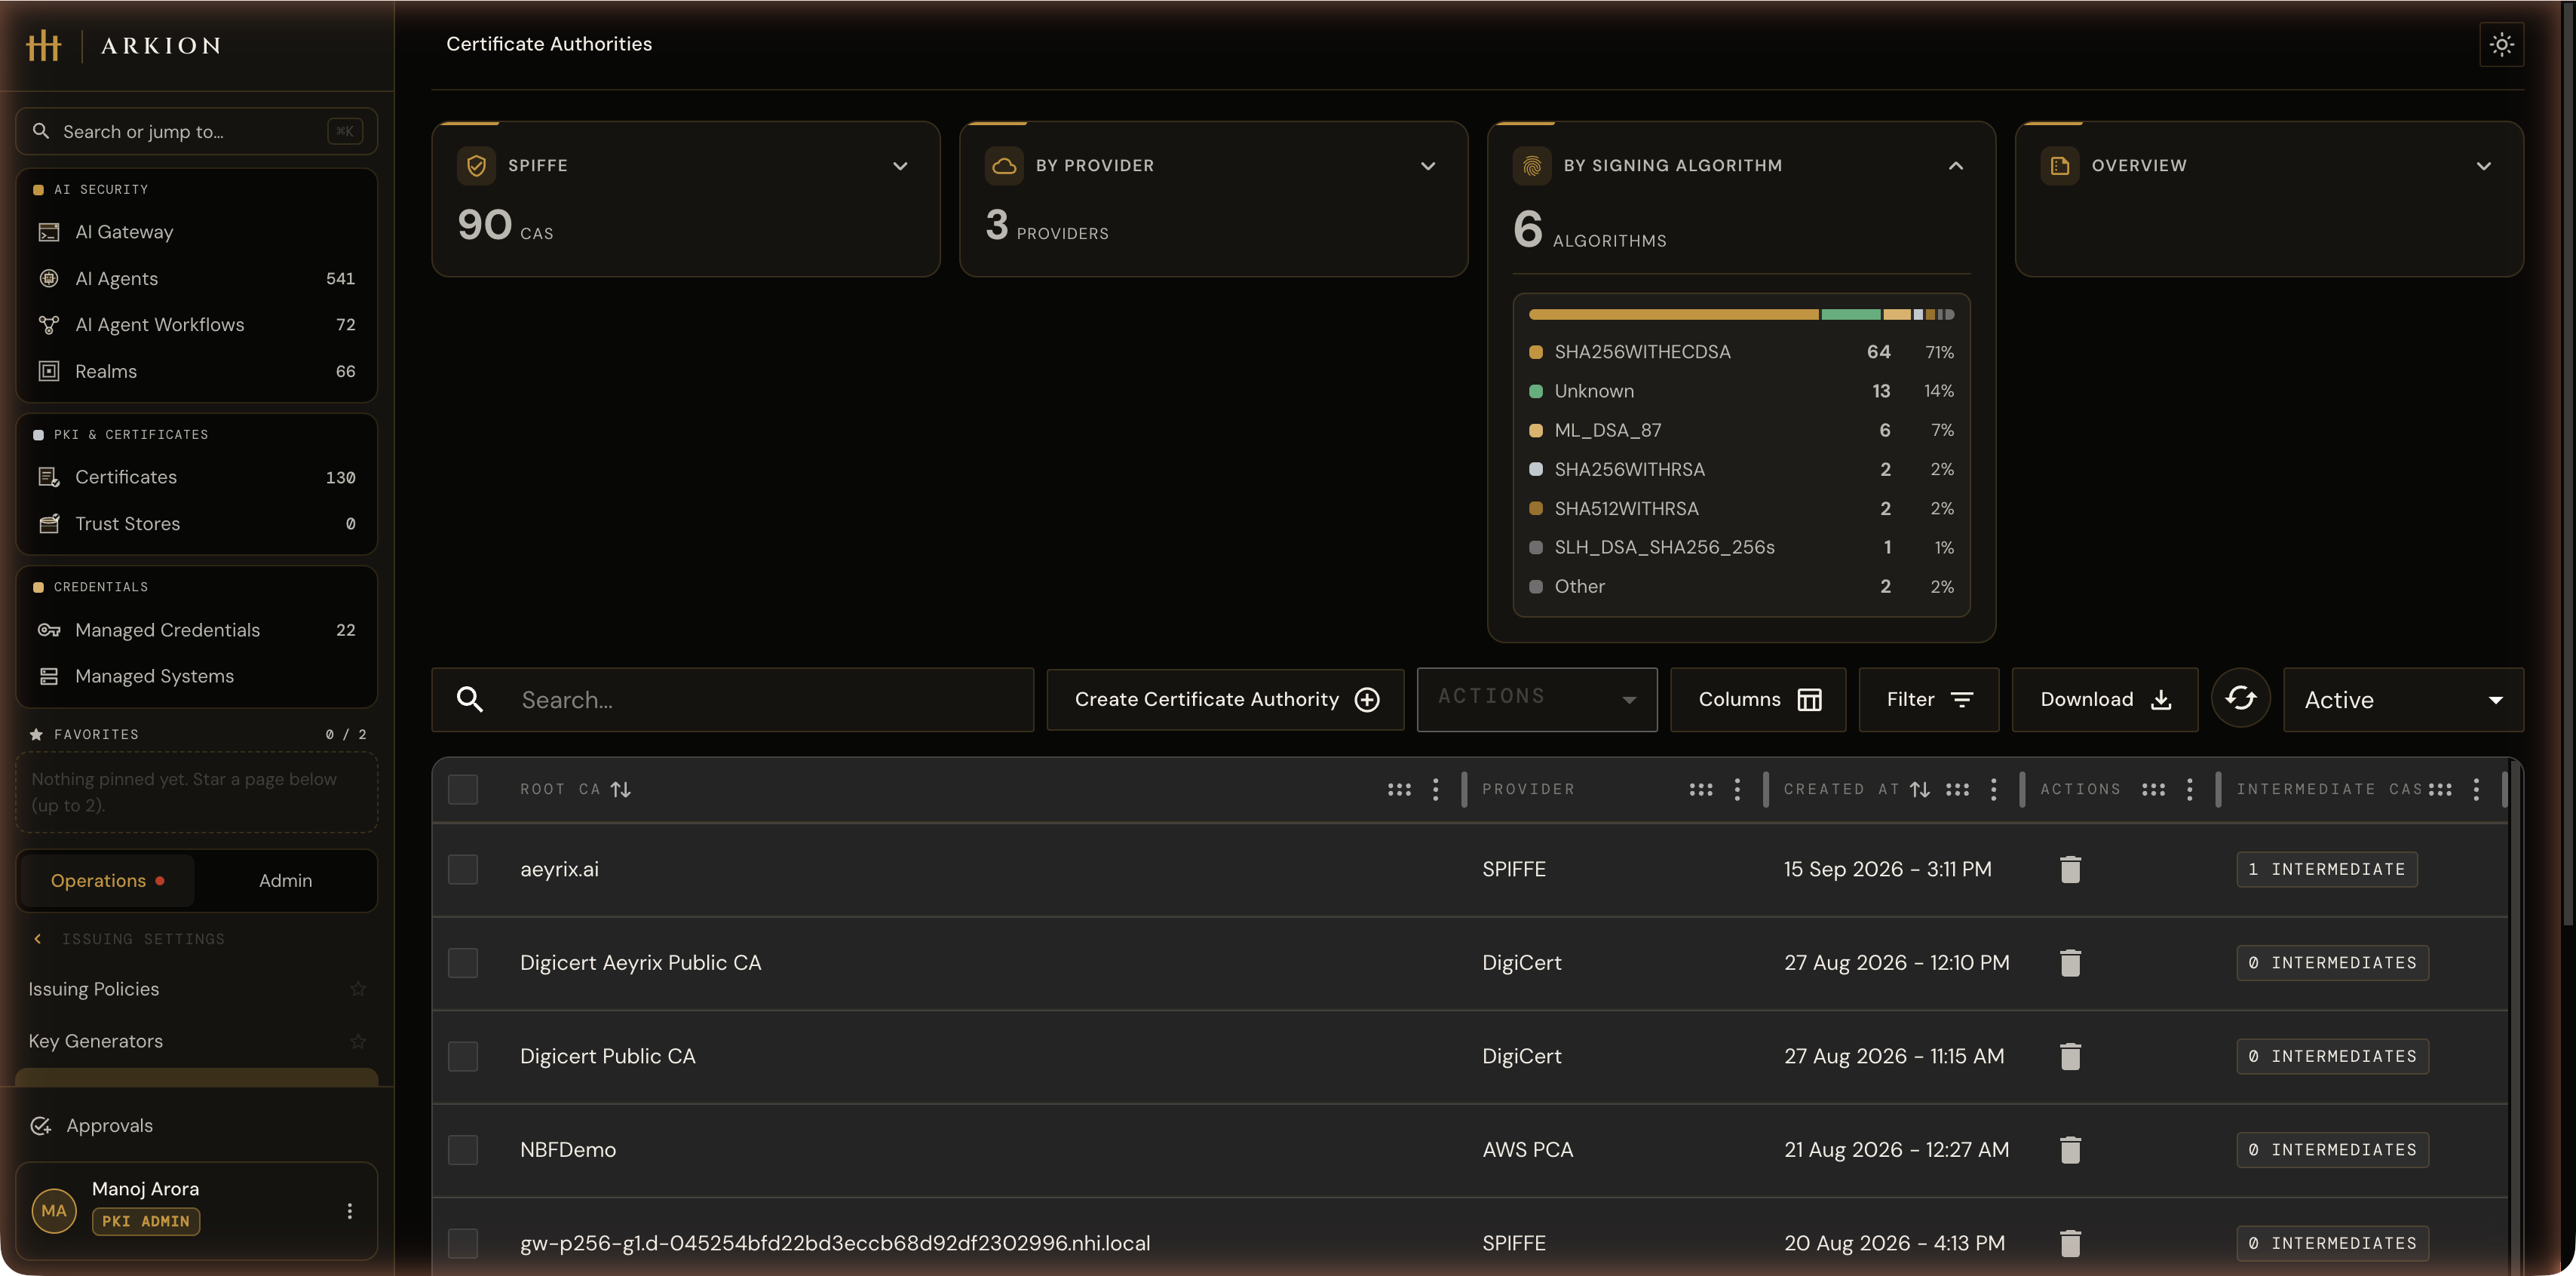
Certificates are issued by a certificate authority. Use Arkion as yours, or keep using DigiCert or AWS Private CA. ArkionID manages all of them together, so you do not have to change providers to get one view.
Ready for quantum computers
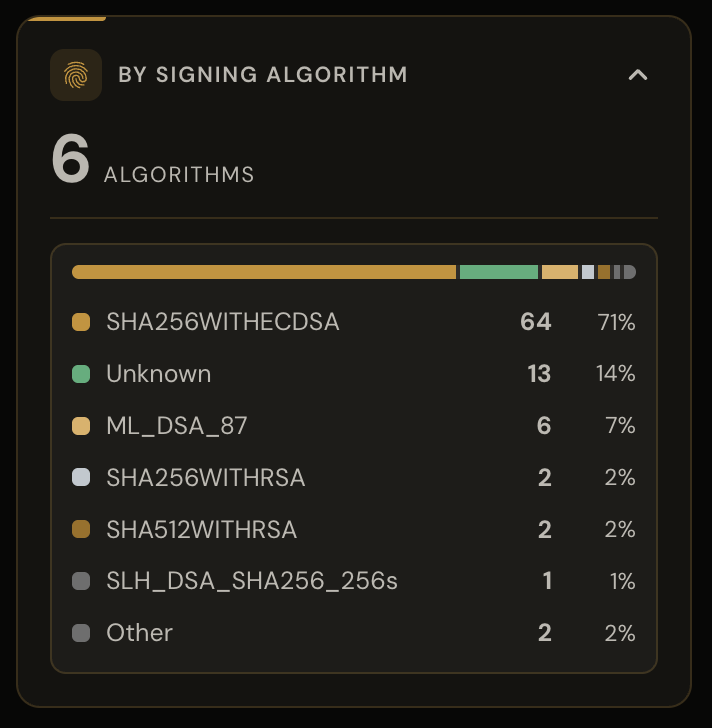
Quantum computers are expected to break the encryption most companies use today. ArkionID already issues certificates using the new quantum-safe methods approved by NIST, the US standards body. They run side by side with the methods you use now, so you can move at your own pace.
Your keys stay in your vault
Every certificate has a secret key behind it. With ArkionID that key can stay in your own Azure Key Vault or AWS KMS, so it never has to leave your control.
One place to run it all
Certificates, certificate providers, issuing rules, keys and cancelled certificates, all managed from one product.
Automatic delivery to your servers
Next, ArkionID will install renewed certificates directly onto the servers, load balancers and clusters that use them, then check they are working, with no manual step in between.
The same engine, pointed at AI agents.
AI agents need IDs too, and they need them far faster than any server. AgentID uses ArkionID to give every AI agent its own short-lived ID and check every action it takes.
See AgentID→